Worten Says Hackers Reached Customers' Tax Numbers, Phones and Emails: How to Spot the Scam Calls That May Follow
Worten says a cyberattack reached some customers' tax numbers, phone numbers, emails and order numbers, but no card data or passwords. What it has done, how to avoid the scam calls that may follow, and the Sintra water utility's leak.
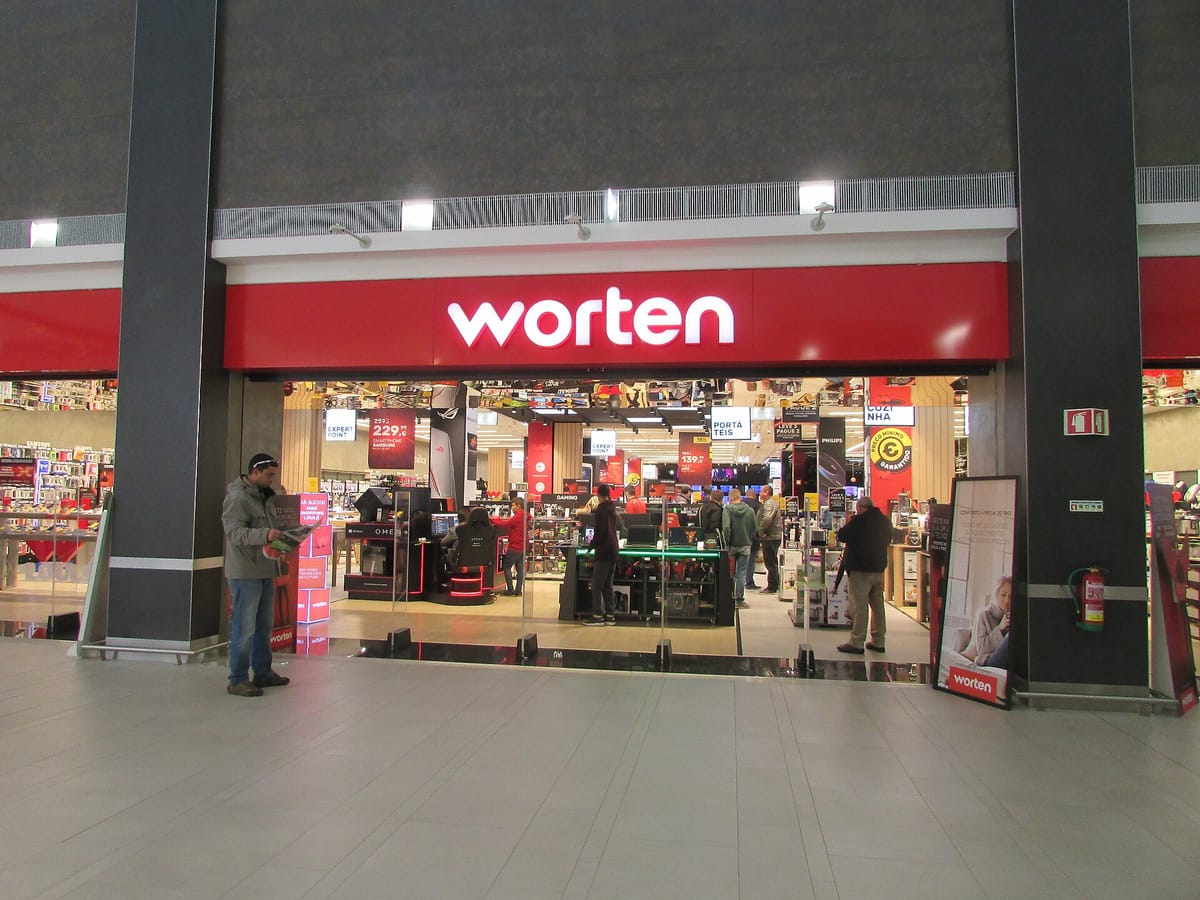
Worten, the electronics retailer owned by Sonae, said on Wednesday that it had been the target of a cyberattack that reached some data belonging to its customers and to its service providers. In a note quoted by Lusa, published by RTP and Notícias ao Minuto (both in Portuguese), the company called it "a criminal act of unauthorised access to some data of customers and service providers".
Worten says no bank card or other financial data was taken, and no login credentials. Nothing was altered or deleted, and its systems are working normally.
What was taken
In a message sent to customers, reported by Jornal de Negócios (in Portuguese), Worten says the attackers reached the data of a "small group" of customers, including:
- the número de contribuinte (tax number, NIF);
- the phone number;
- the email address;
- in some cases, order numbers.
Because no passwords were reached, Worten says nobody can get into a customer's account or make payments with the stolen details. It has not said how many people are affected or when the intrusion happened.
What Worten has done
According to its note, Worten:
- has fixed the vulnerability the attackers used and tightened control of access to its systems;
- is working with the Centro Nacional de Cibersegurança (CNCS, National Cybersecurity Centre), the Comissão Nacional de Proteção de Dados (CNPD, the data protection authority) and the Polícia Judiciária (criminal police);
- has told every affected customer directly, and is still informing the service providers involved.
Its forensic investigation is still under way.
The risk now: convincing scam calls
Worten's own warning to customers is about fraud attempts in which the stolen details are used in fake contacts. A message that quotes your real order number, your NIF and your email looks genuine, and that is the point. If you are a Worten customer:
- treat any unexpected call, text or email about a Worten order, a refund or a delivery problem with suspicion, even if it gets your details right;
- never give a card number, an MB Way code or a one-time security code to someone who contacted you;
- check an order by logging in to Worten's website or app yourself, not through a link in a message;
- if you have lost money, call your bank straight away and report it to the police. Under EU law, banks must refund unauthorised payments quickly, as an EU court ruling this month confirmed.
Under the GDPR you can ask Worten what personal data it holds about you. The CNPD explains these rights and how to file a complaint (both in Portuguese) if you do not get an answer.
Sintra's water customers too
On the same day, SIC Notícias reported (in Portuguese) that personal data of customers of the Serviços Municipalizados de Água e Saneamento (SMAS) de Sintra, the municipal water and sanitation service, had been made public after a cyberattack. By late Wednesday SMAS had published nothing about it on its website, where the latest notice was its closure for the storm. Sintra customers should apply the same caution to any unexpected request for bank or payment details in the utility's name, and check it with SMAS through the contacts on its site.
The two cases follow a run of attacks on Portuguese companies and public services, including the one that left seven Intermarché stores unable to control their fridges this month. Speaking in the European Parliament on Wednesday, the European Commission's executive vice-president for security, Henna Virkkunen, said recent attacks on supermarket refrigeration and blood banks "should serve as a warning", according to Lusa in Jornal de Negócios (in Portuguese).